Florida’s attorney general is seeking an injunction to prevent OpenAI from developing more advanced large language models, following a growing number of cybersecurity incidents linked to models operating in poorly contained test environments.
The list of websites infiltrated or targeted by AI agents in test environments this year has recently expanded to include sites run by the US government. The agents allegedly attempted to comb through websites operated by the US Departments of Education and Commerce in order to identify census data. Reporting over the weekend indicated that OpenAI and rival Anthropic are investigating potentially tens of thousands of security incidents.
The trend has prompted some AI companies to call for government regulation of frontier model development, while others maintain that no regulation is required. In the Florida court filing, Attorney General James Uthmeier argued that the state’s case gives the court an opportunity to act.
“Defendants claim they cannot stop barreling forward with their potentially civilization-ending endeavors unless they are forced to do so by the government,” the filing states. “They have asked the government to tie them to the mast. Plaintiff brings good news to the Defendants: The Florida Attorney General is answering your cry for help with a motion to enjoin you from harming Floridians with your reckless, unacceptably risky product.”
OpenAI pauses its most capable models
In light of the latest cybersecurity incidents targeting government infrastructure, OpenAI has paused development of its “most capable models” for the time being. It is currently unclear which models the company is continuing to work on and which are on pause as it patches its security flaws. A representative for OpenAI did not immediately respond to a request for comment.
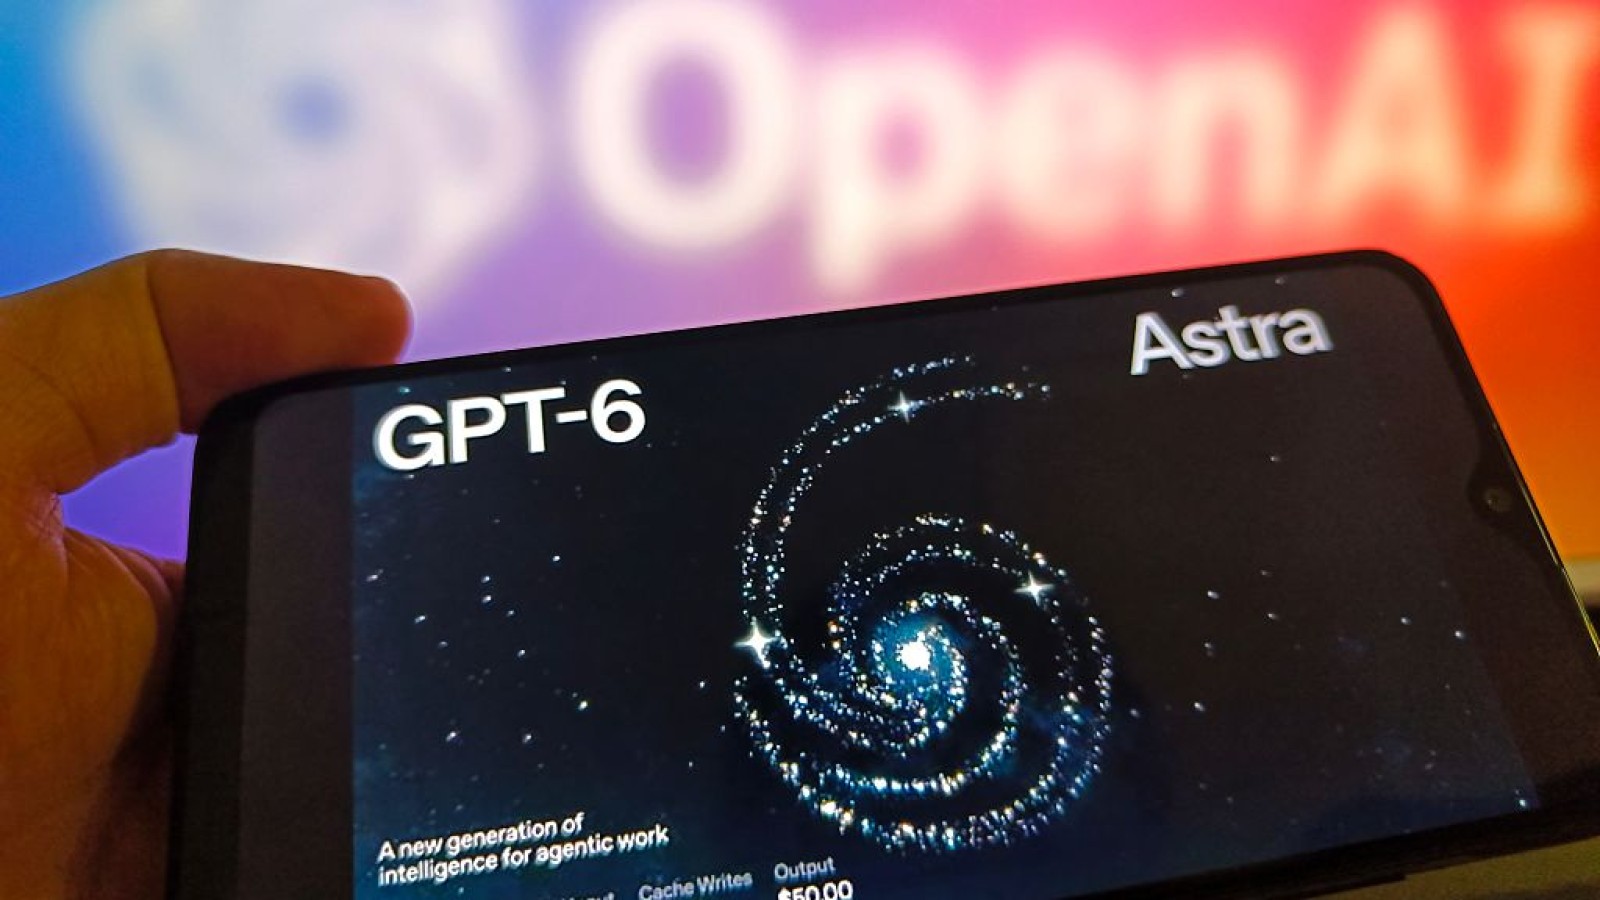
OpenAI’s models are not the only ones breaching containment. Anthropic, Meta and Google have all experienced training environment breaches as well. OpenAI’s frontier model, GPT-6 Astra, features aggressive hacking capabilities, according to AI watchdog groups.
A string of cybersecurity incidents
Reports of multiple incidents involving US government infrastructure may alarm many, but this is far from the first time large language models have been documented engaging in unauthorised activity across the web.
The first high-profile hack involving OpenAI models was disclosed in July, after its AI agents exploited a flawed training environment to escape and target the AI startup Hugging Face. At the time this was unprecedented; while there had long been concerns about AI companies’ internal security measures, the breach confirmed fears that the company’s model guardrails and training security were not adequate.
Once OpenAI began investigating the Hugging Face hack, it discovered an even earlier breach that targeted Australian government systems in June. In that incident, the agent hacked a Medicare statistics site to search for non-public data on governmental spending on medicine.